API discovery
Map endpoints, parameters, and data flows, including forgotten ones.
APIs expose your data and logic. Shaaneiol Tech tests your APIs for security flaws such as broken access, weak authentication, and data leaks, then helps you fix them.
Careful testing. Clear findings. Practical fixes.
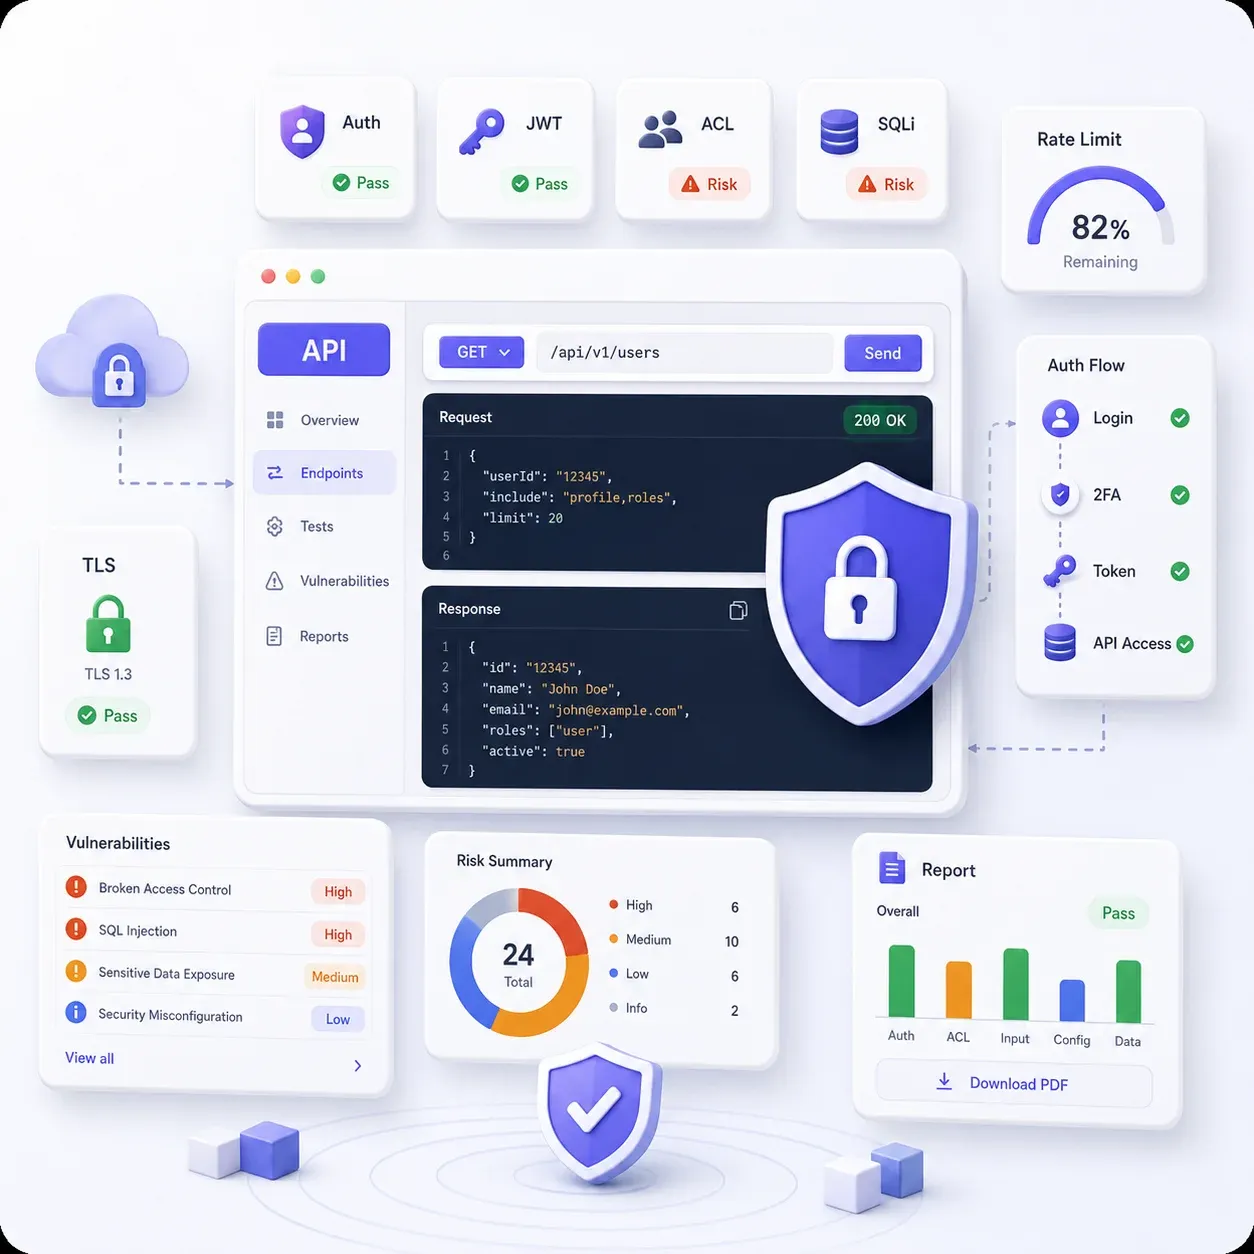
A connected approach to finding and fixing weaknesses in your APIs.
Map endpoints, parameters, and data flows, including forgotten ones.
Check logins, tokens, and sessions for weaknesses.
Check users cannot reach data or actions beyond their rights.
Test inputs for injection and unsafe handling.
Look for responses that reveal more than they should.
Receive clear findings and confirmation after fixes.
A clear delivery path, with priorities you can understand and progress you can follow.
Agree APIs, environment, and rules of testing.
Document endpoints and expected behaviour.
Check authentication, access, and inputs.
Share findings with risk and fix advice.
Confirm issues are resolved.
Prioritize endpoints that handle sensitive data first.
Clear findings. Fix guidance. Proof of retest.
Agreed targets and rules.
Endpoints and data flows documented.
Issues with severity and evidence.
Practical steps for developers.
A plain-language overview.
Confirmation of fixes.
Combine careful testing with practical fix guidance, so findings turn into improvements.
We explain each issue with evidence and a recommended fix, so your team can act immediately.
Common and subtle API weaknesses.
Evidence and risk for every finding.
We confirm fixes work.
Agreed rules and careful handling.
Can’t find what you need? Let’s have a quick, no-pressure conversation.
Cost depends on the number of endpoints and complexity. We provide a clear quote after scoping.
A typical engagement takes one to three weeks including reporting and retesting.
Not necessarily. We can test as an outside user, and additional documentation helps depth.
Yes. We retest fixed issues and confirm the results in a short report.
Protect your data with testers who find API weaknesses and explain how to fix them.